Enable multiple SSL vhosts on a single IP with Apache
Original illustration: Apache with ssl certificate = https — the image file was not found in the original dataset.
Years ago, enabling HTTPS with multiple SSL certificates on Apache port 443 seemed difficult. SNI, or Server Name Indication, makes it much easier by allowing virtual hosts to use different SSL certificates on a single IP address + port 443. SNI still has a limitation: not every browser version supports it, although all newer browsers do. See the supported versions below.
- Opera 8.0+ (with TLS 1.1 enabled)
- Firefox 2+
- Internet Explorer 7+
- Safari 3.2.1+ on Vista or higher and Mac OS X 10.5.6 or higher
- Chrome (NOT Chromium) on Vista or higher
Apache has two modules for configuring HTTPS with multiple SSL certificates on port 443, or SNI: the SSL module (mod_ssl) and mod_gnutls. The difference is that mod_ssl requires Apache 2.2.8 or later, while mod_gnutls is an additional module and does not require Apache 2.2.8. Configuring SSL virtual hosts is similar to configuring ordinary virtual hosts: change the port from 80 to 443 and enable the SSL certificate. This article gives examples of both mod_ssl and mod_gnutls configuration. Follow these steps: Enable multiple SSL vhosts with mod_ssl
-
Configure Apache to listen on port 443, set NameVirtualHost, and load mod_ssl in /etc/http/conf.d/ssl.conf.
Listen 443 NameVirtualHost *:443 ... LoadModule ssl_module modules/mod_ssl.so -
Add the VirtualHost configuration below at the end of /etc/http/conf.d/ssl.conf, or another configured location. Adjust the certificate file paths, ServerName, and other settings for your website.
<VirtualHost *:443>
    SSLEngine on
    SSLCertificateFile /etc/apache2/ssl/server1.crt
    SSLCertificateKeyFile /etc/apache2/ssl/server1.key

    ServerName secure.ezylinux.com
    DocumentRoot /path/to/www/site1
    <Directory /path/to/www/site1>
        SSLRequireSSL
        Order Deny,Allow
        Allow from All
    </Directory>
</VirtualHost>

<VirtualHost *:443>
    SSLEngine on
    SSLCertificateFile /etc/htt/ssl/server2.crt
    SSLCertificateKeyFile /etc/http/ssl/server2.key

    ServerName secure.ezylinux.com
    DocumentRoot /path/to/www/site2
    <Directory /path/to/www/site2>
        SSLRequireSSL
        Order Deny,Allow
        Allow from All
    </Directory>
</VirtualHost>
Enable multiple SSL vhosts with mod_gnutls
-
Install gnutls_module with this command (for CentOS 5):
[root@Ezylinux ~]# yum install mod_gnutls --enablerepo=c5-testing -
Configure Apache to listen on port 443, set NameVirtualHost, and add the following to load gnutls_module in /etc/http/conf.d/ssl.conf:
Listen 443 NameVirtualHost *:443 ... LoadModule gnutls_module modules/mod_gnutls.so -
Add the VirtualHost configuration below at the end of /etc/http/conf.d/ssl.conf, and adjust the certificate file paths, ServerName, and other settings for your website.
<VirtualHost *:443>
    GnuTLSEnable on
    GnuTLSExportCertificates on
    GnuTLSCacheTimeout 500
    GnuTLSCertificateFile /etc/http/ssl/server1.crt
    GnuTLSClientCAFile  /etc/http/ssl/CA-bundle1.crt
    GnuTLSKeyFile /etc/http/ssl/server1.key

    ServerName secure1.ezylinux.com
    DocumentRoot /path/to/www/site1
    <Directory /path/to/www/site1>
        Order Deny,Allow
        Allow from All
    </Directory>
</VirtualHost>

<VirtualHost *:443>
    GnuTLSEnable on
    GnuTLSExportCertificates on
    GnuTLSCacheTimeout 500
    GnuTLSCertificateFile /etc/http/ssl/server2.crt
    GnuTLSClientCAFile  /etc/http/ssl/CA-bundle2.crt
    GnuTLSKeyFile /etc/http/ssl/server2.key

    ServerName secure2.ezylinux.com
    DocumentRoot /path/to/www/site2
    <Directory /path/to/www/site2>
        Order Deny,Allow
        Allow from All
    </Directory>
</VirtualHost>
Once configured, test in a browser by visiting https://secure1.ezylinux.com and https://secure/.ezylinux.com, or use OpenSSL’s s_client by running:
[root@Ezylinux ~]# openssl s_client -connect secure1.ezylinux.com:443
[root@Ezylinux ~]# openssl s_client -connect secure2.ezylinux.com:443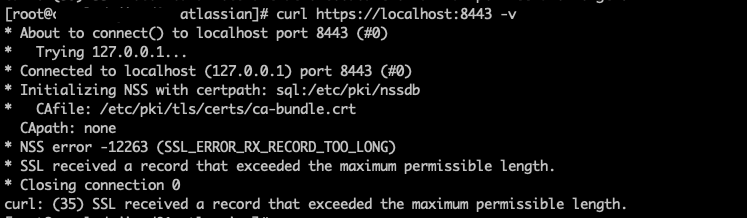
Archived comments (1)
Preserved from the original blog for reference.
Historically, if you wanted to [host multiple SSL enabled Web sites](/en/enable-multiple-ssl-vhosts-and-certificates-on-a-single-ip-with-apache/), you had to have an unique IP address for each site....