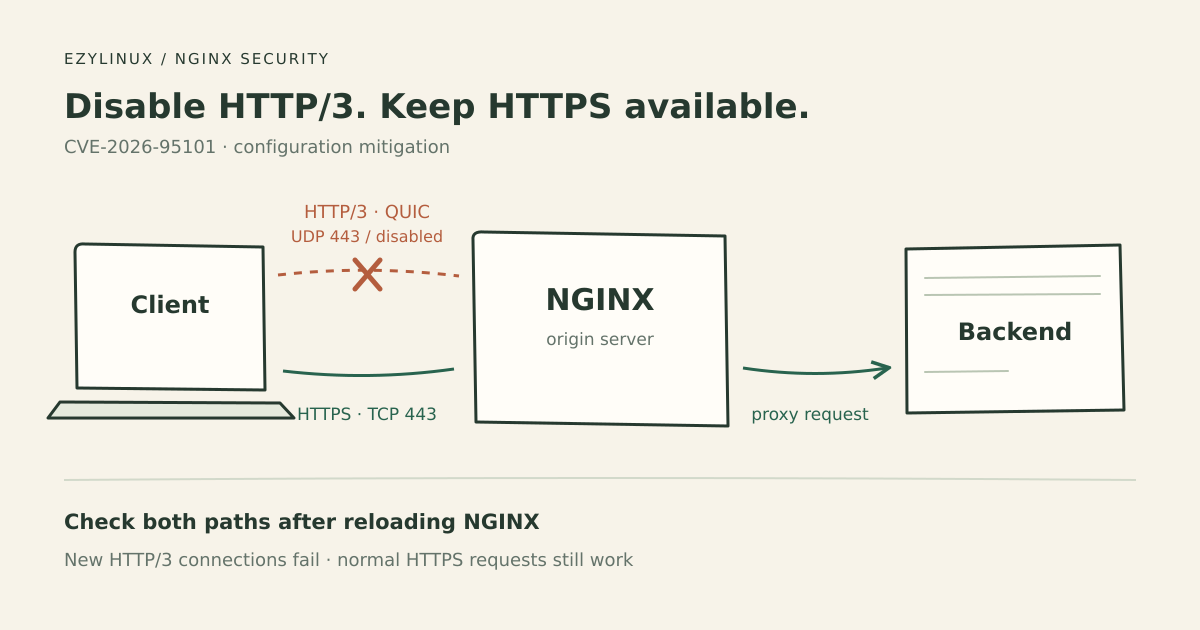
Disable NGINX HTTP/3 for CVE-2026-95101 and verify the change
Disable NGINX QUIC listeners to mitigate CVE-2026-95101, compare HTTP/3 and HTTPS before and after, and understand the request-buffering alternative.
1 articles on this topic
Disable NGINX QUIC listeners to mitigate CVE-2026-95101, compare HTTP/3 and HTTPS before and after, and understand the request-buffering alternative.